
New $13 Million Cybersecurity Settlement Highlights Evidence Risk for Federal Contractors
News originally published by
EIN Presswire
Lazarus Alliance Proactive Cyber Security services Logo
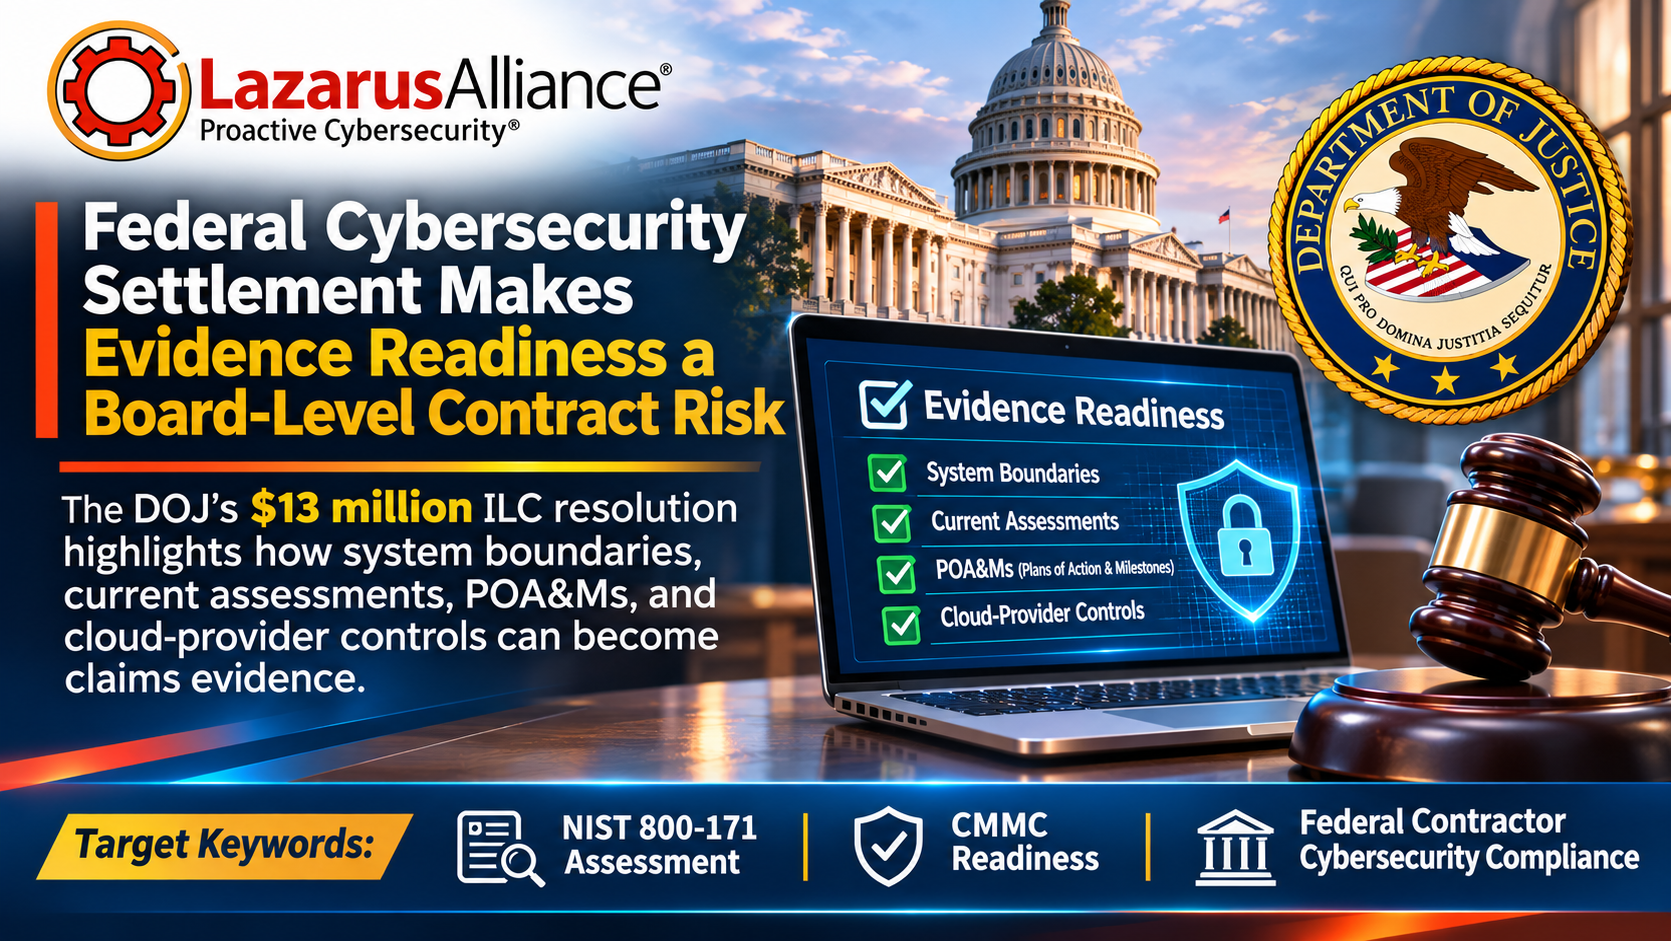
Federal Cybersecurity Settlement Makes Evidence Readiness a Board-Level Contract Risk
Lazarus Alliance outlines why assessments, accurate system boundaries, disciplined remediation records, cloud-provider oversight require executive attention.
The DOJ announcement and settlement agreement describe allegations involving incomplete implementation of controls in NIST Special Publications 800-171 and 800-53, missing or outdated system security plans, absent plans of action and milestones during specified periods, and assessment records that were not current or had not been submitted. The government also alleged that controlled defense information was stored with an external cloud provider without ensuring contractually required protections, including requirements equivalent to the FedRAMP Moderate baseline and specified incident-response obligations.
For federal contractors and subcontractors, the practical issue extends beyond whether a policy exists. Executives need confidence that the applicable contract clauses have been identified, covered systems and data flows are accurately scoped, assessment results reflect the actual environment, deficiencies are governed to closure, and representations to customers or government systems remain supportable as technology and suppliers change.
An evidence-readiness review can connect those obligations to system diagrams, inventories, control narratives, test results, risk decisions, supplier records, POA&Ms, and management approvals. That record also needs disciplined change control so a migration, acquisition, new cloud service, or altered data flow does not silently invalidate an assessment or system security plan.
Lazarus Alliance supports organizations with cybersecurity audit and compliance, risk assessment and management, policies and governance, CMMC readiness, NIST-aligned control evaluation, and Cybervisor® advisory services. The appropriate scope depends on the specific contract, information handled, system boundary, and assessment requirement; organizations should obtain qualified legal advice on contractual and False Claims Act questions.
“This settlement is a reminder that cybersecurity commitments become business records. Leaders should be able to trace each material representation to a defined system boundary, current assessment evidence, owned remediation work, and documented oversight of every provider that handles regulated or contract-sensitive information. That discipline improves risk decisions and gives the organization a defensible basis for what it says to customers and government agencies.” — Michael Peters, CEO & Founder, Lazarus Alliance
ABOUT LAZARUS ALLIANCE
Lazarus Alliance is a veteran-owned global provider of Proactive Cybersecurity®, specializing in cybersecurity audit and compliance, risk assessment and management, privacy audit and compliance, vulnerability and penetration testing, and IT policies and governance. Founded in 2000, the firm helps organizations attain, maintain, and demonstrate information security and compliance excellence across complex regulatory environments.
Lazarus Alliance is an authorized CMMC Third-Party Assessment Organization (C3PAO), an A2LA-accredited FedRAMP Third-Party Assessment Organization (3PAO), and a PCI DSS Qualified Security Assessor (QSA). Headquartered in Scottsdale, Arizona, Lazarus Alliance serves organizations ranging from startups to multinational enterprises with cybersecurity, privacy, risk, governance, and compliance expertise.
Michael Peters
Lazarus Alliance, Inc.
+17628224174 ext.
Visit us on social media:
LinkedIn
YouTube
X
About Lazarus Alliance
Legal Disclaimer:
EIN Presswire provides this news content "as is" without warranty of any kind. We do not accept any responsibility or liability for the accuracy, content, images, videos, licenses, completeness, legality, or reliability of the information contained in this article. If you have any complaints or copyright issues related to this article, kindly contact the author above.
